Léo Grambert

Web developer turned application security researcher.

Eight years building and shipping web applications, now spending that knowledge on breaking them. I report what I find, publish the proof, and turn it into material other people can learn from.

Advisories & research

2 advisories · 3 PoCs

Vulnerabilities I found and disclosed to maintainers, the exploit code I published, and what I have written about it.

GHSA-g747-7v24-2w4v

Medium

OAuth2 state parameter is not validated on callback, allowing authorization code injection

usebruno/bruno

Read the findingHide the finding

When using the "Use system browser for OAuth" option, Bruno did not validate the OAuth2 state value returned on the callback against the value it issued. This could allow an authorization code from a different OAuth2 flow to be accepted on the callback, which is the scenario the state parameter is designed to prevent (OAuth2 CSRF / authorization code injection).

The state validation applies to both the Authorization Code and Implicit grants. The issue is fixed in v4.0.0.
CVE-2026-32255

High 8.6

Unauthenticated SSRF in attachment download endpoint

kanbn/kanGHSA-qrx8-9hc6-jvqg

Read the findingHide the finding

Kan is an open-source project management tool. In versions 0.5.4 and below, the /api/download/attatchment endpoint has no authentication and no URL validation. The Attachment Download endpoint accepts a user-supplied URL query parameter and passes it directly to fetch() server-side, and returns the full response body. An unauthenticated attacker can use this to make HTTP requests from the server to internal services, cloud metadata endpoints, or private network resources. This issue has been fixed in version 0.5.5. To workaround this issue, block or restrict access to /api/download/attatchment at the reverse proxy level (nginx, Cloudflare, etc.).

Exploit code, other people's findings

  • CVE-2025-55182

    This repository contains a POC of CVE-2025-55182, a critical (CVSS score 10.0) pre-authentication remote code execution vulnerability affecting React Server Components, also known as React2Shell.

    ★ 15 · ⑂ 3
  • CVE-2025-29927

    This repository contains a POC and an exploit script for CVE-2025-29927, a critical vulnerability in Next.js that allows attackers to bypass authorization checks implemented in middleware.

    ★ 8 · ⑂ 3

Writing

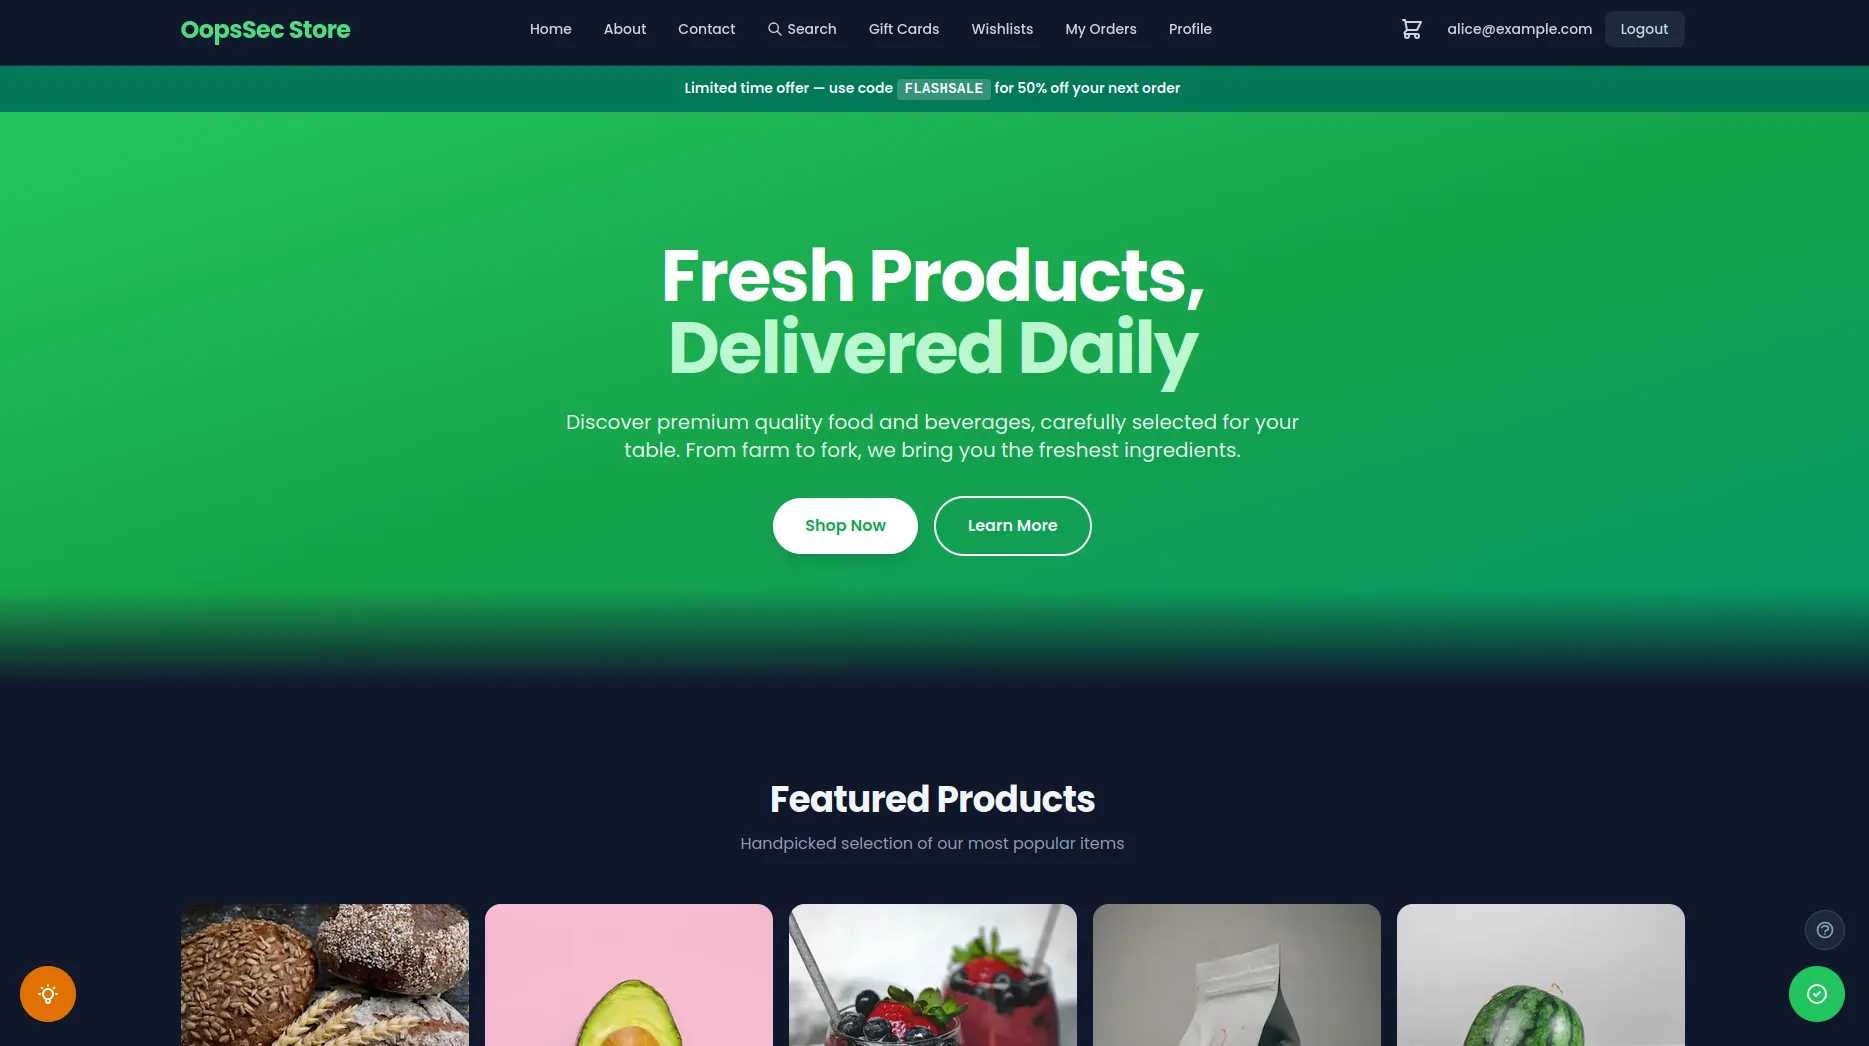
OopsSec Store

★ 45 · ⑂ 55

A deliberately vulnerable application I build and maintain, used to teach application security.

Security training for the apps you actually ship.

A deliberately vulnerable Next.js storefront with 36 challenges spanning web, API, authentication, business logic, cryptography, supply chain and AI agents. Listed in the OWASP Vulnerable Web Applications Directory and used as a TryHackMe room.

Open the OopsSec Store walkthroughsThe OopsSec Store storefront: a deliberately vulnerable e-commerce site, shown logged in as a demo user.

Other projects

  • cyber-bot

    Telegram bot for cyber watch (CVEs, RSS, podcasts, AI summaries).

    ★ 7
  • crack-hash

    A fast, multi-threaded hash cracking tool written in Rust. This tool performs dictionary attacks against hashed passwords.

    ★ 2
  • hate-crimes-map

    This project aims to visualize hate crime data to bring visibility to crimes that are often invisible or normalized by society.

    ★ 3
  • awesome-pentest-tools

    Open-source offensive security tools, plus a vendor-agnostic AI agent that runs authorized pentest engagements using only tools from this list.

    ★ 3

Open source

22 repositories
  • kanbn/kan

    TypeScript★ 5.7k

    The open source Trello alternative.

    Reported and helped fix an unauthenticated SSRF (CVE-2026-32255).

  • usebruno/bruno

    JavaScript★ 47.1k

    Opensource IDE For Exploring and Testing API's (lightweight alternative to Postman/Insomnia)

    Reported an OAuth2 state-validation flaw (GHSA-g747-7v24-2w4v).

  • OWASP/www-community

    HTML★ 1.4k

    OWASP Community Pages are a place where OWASP can accept community contributions for security-related content.

    Authored the MCP Tool Poisoning attack page.

  • OWASP/www-project-vulnerable-web-applications-directory

    HTML★ 94

    The OWASP Vulnerable Web Applications Directory Project (VWAD) is a comprehensive and well maintained registry of all known vulnerable web applications currently available.

    Added OopsSec Store to the directory.

  • ThePorgs/Exegol

    Python★ 3.1k

    Fully featured and community-driven hacking environment

  • beelzebub-labs/beelzebub

    Go★ 2.2k

    A secure low code deception runtime framework, leveraging AI for System Virtualization.

  • OWASP/OCSD

    ★ 41

    OWASP Certified Secure-Software Developer

Also contributed to

Background

Experience

  1. Feb 2018 — Jun 2026

    Full-Stack Web Developer — Hardloop, Remote

    • Built and maintained the e-commerce platform and internal business tools
    • Helped drive a year-long ERP migration with zero-downtime deployment strategies
    • Set up CI/CD pipelines and deployment automation
    • Applied security best practices across the software development lifecycle
  2. Mar 2021 — PresentCurrent

    Web Development Mentor — OpenClassrooms, Remote

    • Mentor students through web development projects, teaching professional best practices
    • Conduct code reviews and provide architectural guidance

Education

  1. 2026 — 2027Current

    Master 2, Information Systems Security (OPSIE) — Université Lumière Lyon 2

    • ANSSI SecNumÉdu-labelled programme covering security governance, risk and audit, cryptography, infrastructure and application security, and IT law.
  2. 2016 — 2017

    Professional Title, Web Development — IESA Multimedia

    • Full-stack web development and software architecture.
  3. 2013 — 2014

    Master 1, Social Law — Jean Moulin Lyon 3 University

    • Graduated with honors. Legal foundation relevant to compliance and incident response.
  4. 2009 — 2013

    Bachelor's Degree, Law — Jean Moulin Lyon 3 University

Volunteering

  1. Jul 2026 — PresentCurrent

    Digital Inclusion Volunteer — Emmaüs Connect, Lyon, France

    • Run one-on-one digital support sessions for people facing digital exclusion, referred by partner social organisations
    • Guide people through online public services, device setup and account recovery, working towards autonomy rather than doing it for them
    • Cover practical digital hygiene: password management, account security and recognising phishing attempts
  2. Aug 2026 — PresentCurrent

    Tech Volunteer — Data for Good, Remote / Lyon, France

    • Member of a volunteer-run, fully open-source tech community that builds digital tools with NGOs on climate, social justice and democracy
    • Contribute web development skills to general-interest projects, from three-month acceleration seasons with partner organisations to community open-source tooling
    • Active in the Lyon chapter and the wider remote community

Tools & technologies

Programming Languages
JavaScript, TypeScript, Python, PHP, Ruby
Web Frameworks
React, Next.js, Node.js, FastAPI, Ruby on Rails, Symfony, Hapi.js
Security
Vulnerability Research, CVE Analysis, CTF Challenges, Web Application Security
DevOps & Tools
Git, CI/CD, Docker, Linux, Shell Scripting
Languages
French (Native), English (B2), German (A2)

Certificates

124 total
Show the remaining 109Hide the remaining 109